

What CPM is
What CSPM did for cloud misconfiguration, CPM does for cryptography
Cloud Security Posture Management made misconfigured buckets and open ports a continuously monitored problem instead of an annual audit finding. Cryptographic Posture Management does the same for keys, certificates and algorithms: a standing inventory that stays current, a score that moves when your estate moves, and a remediation path that closes the loop instead of ending in a spreadsheet. Point-in-time audits tell you where you stood. CPM tells you where you stand, right now, and what to do about it.
The CPM loop
Four stages, running continuously, not once a year
Discover
Every scanner surface, one inventory
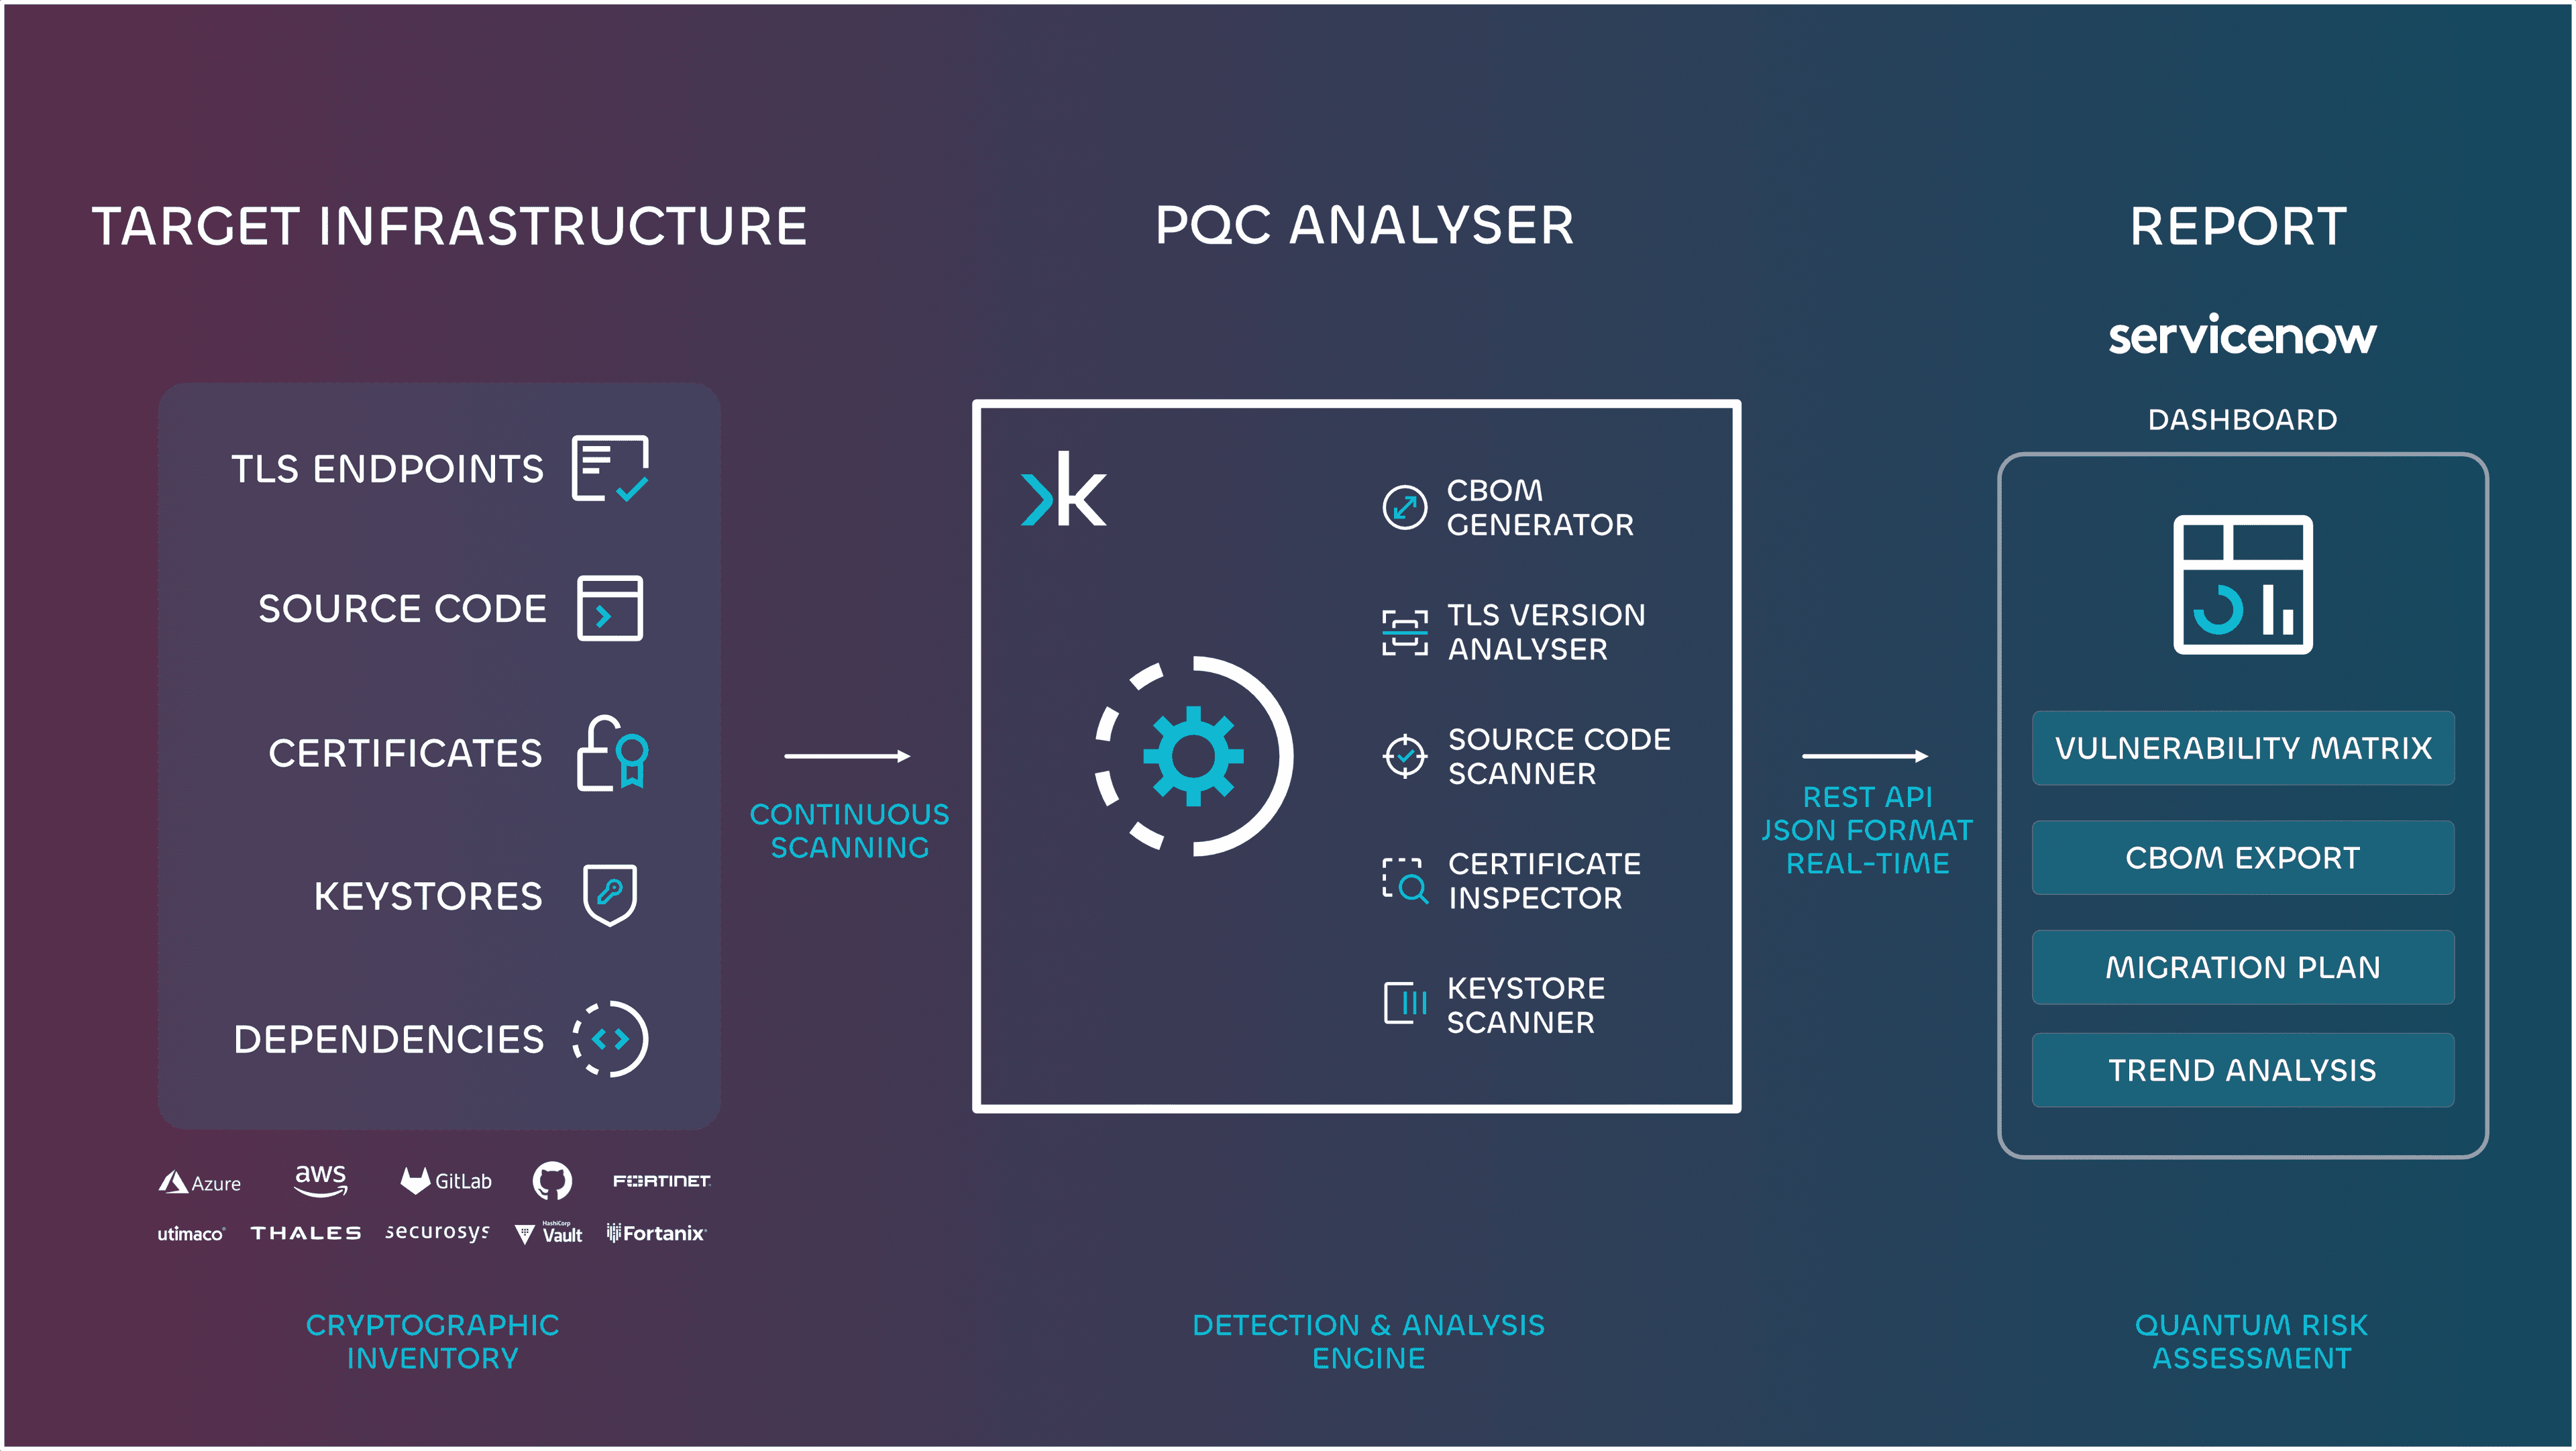
Filesystem, source code, GitHub and GitLab repositories, Terraform IaC, TLS-facing domains, SSH fleets, cloud KMS, identity providers and artifact registries all feed a single CycloneDX-standardised Cryptographic Bill of Materials, not one report per tool.
More on the CBOM ↓Score
Weighted, published, reproducible
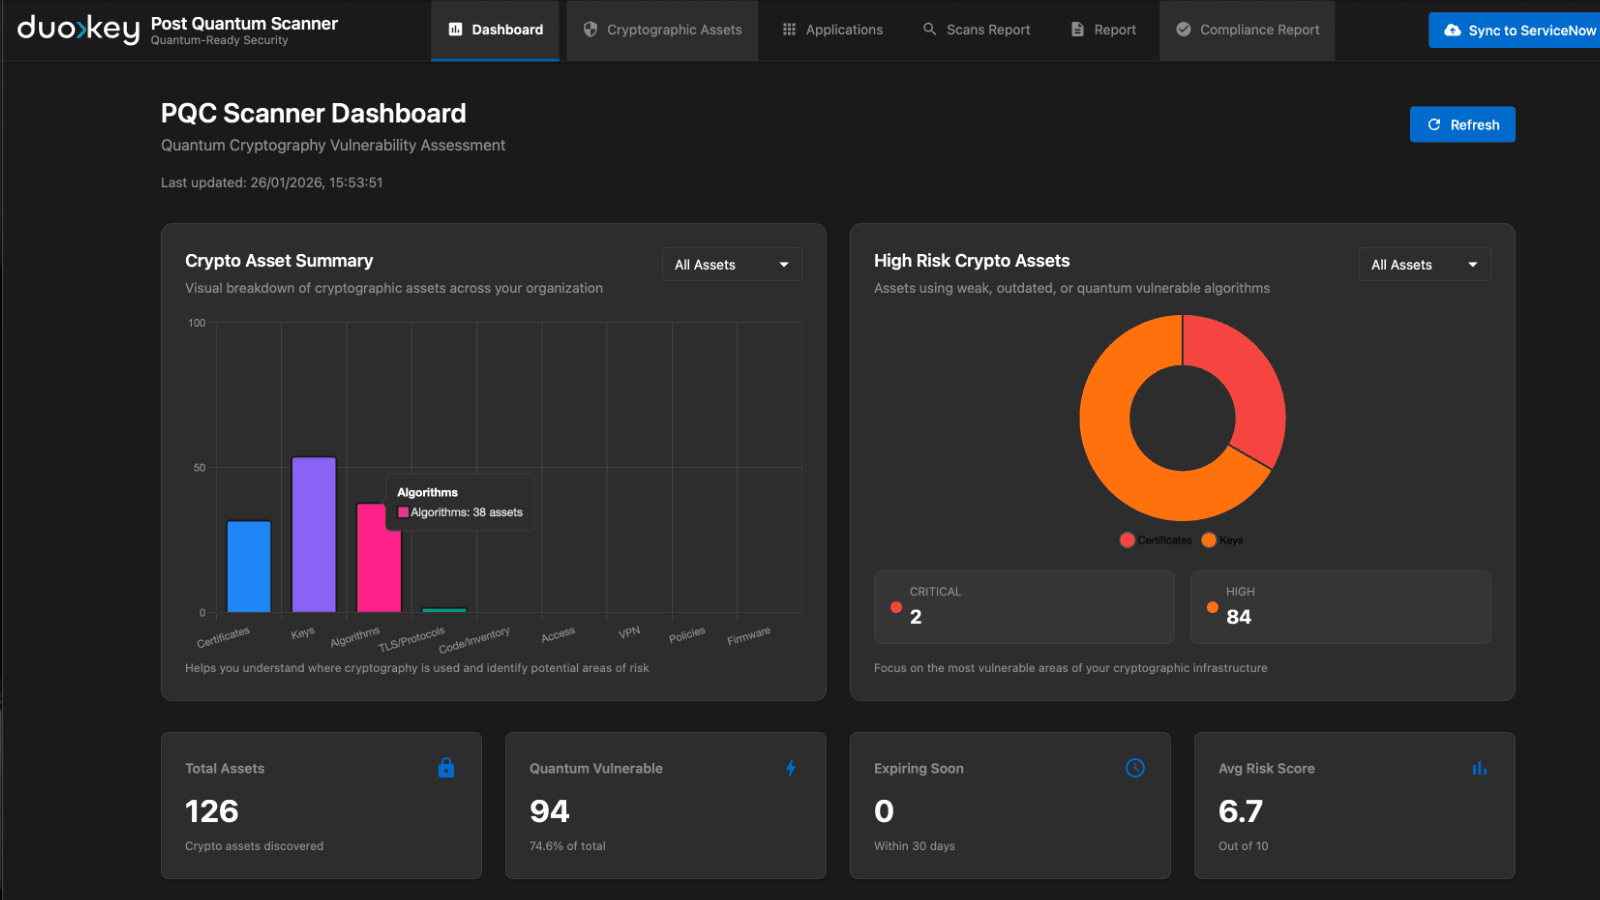
Every discovered asset is scored against a published methodology and checked for drift against your own declared cryptographic policy, so a new RSA-2048 certificate or a quietly downgraded cipher suite surfaces the day it appears, not at the next audit.
The score has its own page → Quantum Risk ScoreSimulate
Test the change before you ship it
Model the blast radius of a policy change, such as requiring ML-KEM-768 on every IPsec gateway, before it touches production. See exactly which assets pass, which fail, and what the resulting score would be, prior to rollout.
Remediate
An agent drafts the fix. A human approves it.
A scoped pull request against the actual target, an F5 profile, a Fortinet gateway, an expiring certificate, drafted automatically and reviewed like any other change. Once merged and deployed, the fix is verified and the finding closes itself.
How the keys behind it are protected ↓The system of record
The CBOM: one inventory, not a spreadsheet before an audit
Every stage of the loop reads from and writes to the same artefact: a Cryptography Bill of Materials, the CycloneDX-standardised inventory of every algorithm, key, certificate and protocol Discover finds. Score compares it against policy. Simulate tests changes against it. Remediate updates it once a fix ships. One living record, queryable through Cockpit or the same MCP tools your agents already use, not a document someone assembles by hand before the next audit.
- CycloneDX 1.7, the OWASP-backed standard for cryptographic inventories
- Every entry traced to source: the file, the repository, the certificate or the gateway it came from
- Updates as the estate changes, not on a scan-and-forget cadence

The keys behind the fix
Remediation runs on keys that are never assembled
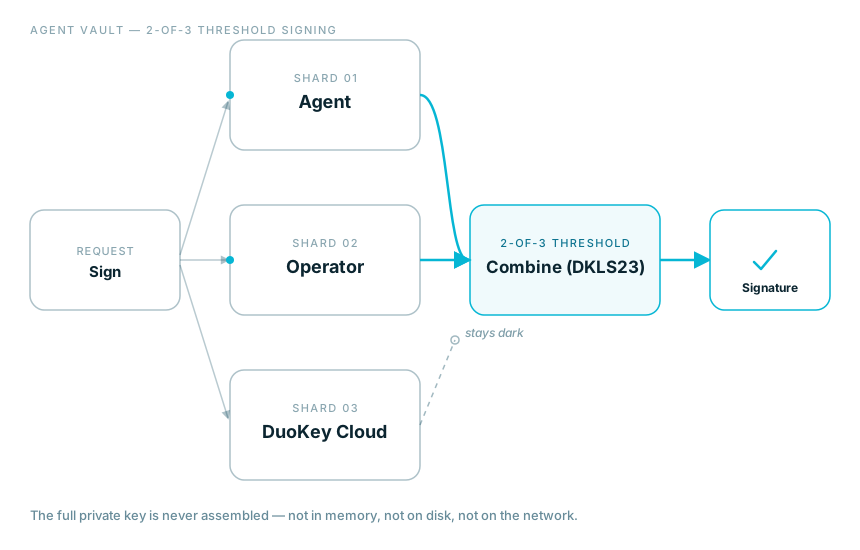
When Remediate issues a new key, a hybrid ML-KEM certificate, a rotated service credential, a fresh signing key, that key is protected the same way every key in DuoKey's KMS is: split across independent shards with multi-party computation (MPC), not held whole inside a single HSM. A 2-of-3 threshold means no single shard, agent, operator or cloud, can produce a valid signature alone, and the full private key is never assembled in memory, on disk or on the network. The fix CPM drafts is only as trustworthy as the key material behind it.
Where the loop starts
Every CPM engagement starts with a number: your Quantum Risk Score
QRS is the discovery-and-scoring stage of CPM, published as its own assessment: a 0-100 composite index against a public methodology, built from your domain's observable signals, no internal access required. It is the first page of the same inventory that feeds simulation and remediation once you go deeper.
Where it plugs in
Discovery reaches the estate you actually run


Deliverables
Output built to be used, not filed away
- 01A living CBOM, not a snapshot
A CycloneDX-standardised Cryptographic Bill of Materials that updates as your estate changes, queryable through Cockpit or the same MCP tools your agents already use.
- 02Drift alerts
A gap between your declared cryptographic policy and what is actually deployed, flagged the day it opens, not discovered at the next audit cycle.
- 03Simulation reports
The projected effect of a proposed policy change on your score and on every affected asset, before you commit to rolling it out.
- 04Remediation pull requests
Scoped, reviewable changes against the real target infrastructure, with a named owner and a full audit trail from finding to merged fix.
- 05ServiceNow synchronisation
Findings, drift and remediation status sync into the ITSM workflows your teams already use, instead of living in a separate dashboard nobody checks.
- 06Regulatory mapping
Posture mapped against DORA, NIS2, FINMA 05/2026, NIST IR 8547 and CNSA 2.0, so one inventory answers every regulator asking the same underlying question.
A one-off scan tells you what was true on the day you ran it. A posture that stays current is a standing capability.
DuoKey runs the full loop, discovery, scoring, simulation and remediation, as one platform, so your cryptographic posture is something you monitor, not something you rediscover every audit cycle.
Certification
ISO/IEC 27001:2022, recertified 2024
Deployments
30+ enterprises across automotive, Swiss banks, EU telcos
Recognition
InCyber Forum 2024, Growth Startup Award
Standards
CycloneDX, SPDX, OWASP-aligned
Engagement
Start with a score, end with a closed loop
Get your Quantum Risk Score first, free and requiring no access to internal systems, then talk to us about running the full discovery, simulation and remediation loop across your estate.
Get your Quantum Risk Score